Today · October 14
AWS's Kiro adds an OS sandbox; no third party measured it
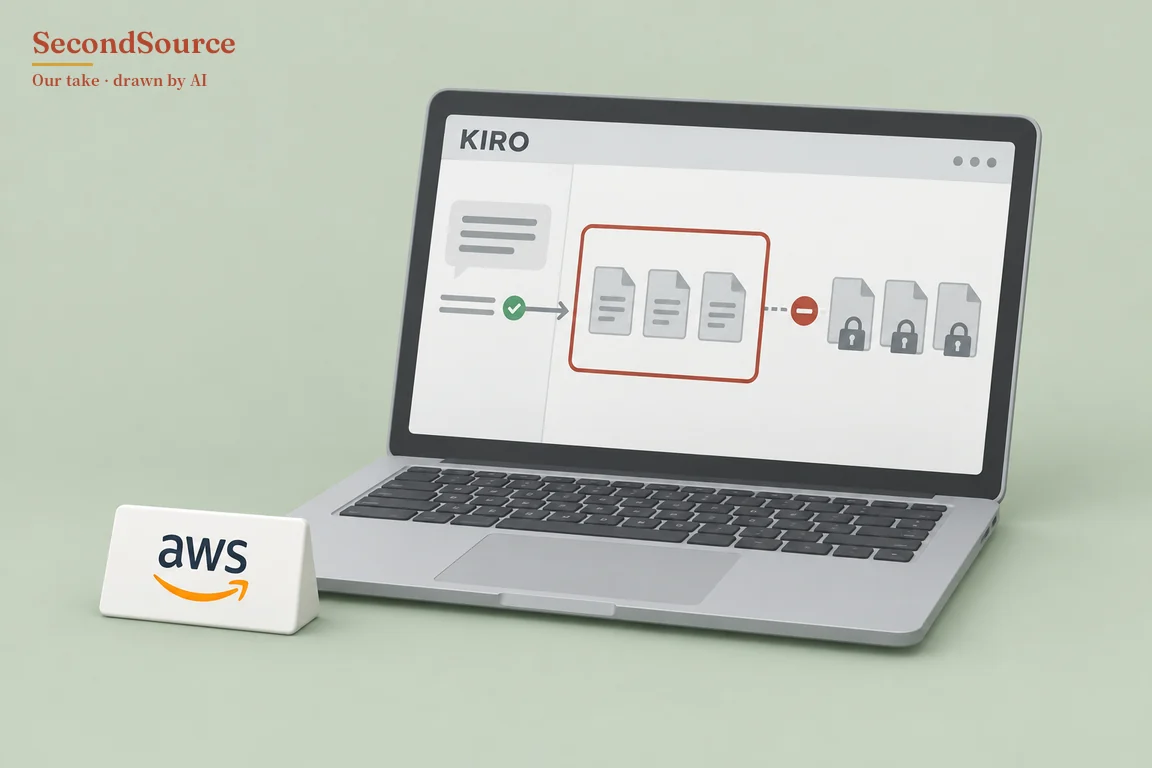
Kiro, AWS's development environment for coding agents, adds a local sandbox: even after a command is approved to run, the operating system still limits which files it can read and write. Swami Sivasubramanian, AWS's vice president for agentic AI, wrote: "even after a command is approved, the operating system still limits what it can read and write" (Swami Sivasubramanian, 2026-10-14). Kiro's blog says it uses the isolation mechanisms built into macOS, Linux and Windows, that the feature is off by default, and that network traffic goes through a local proxy filtered by domain (Kiro blog, 2026-10-14). The stated reason is that when several agents run at once, approving commands one by one doesn't scale. The agent program itself still sits outside the sandbox, and the effect has no third-party measurement. How we checked →
Source and checks
This item ran in the brief of Oct 15, 2026, alongside 18 other items. How we checked it, the quote checks and what was still missing that day are on that issue's How we checked page.
Cite this item
SecondSource (2026). "AWS's Kiro adds an OS sandbox; no third party measured it." https://secondsource.io/en/product/2026-10-15-2/. Accessed access date.