OpenAI says its newer cybersecurity model found 948 Linux kernel flaws that grant root, against 166 for the model it used in July
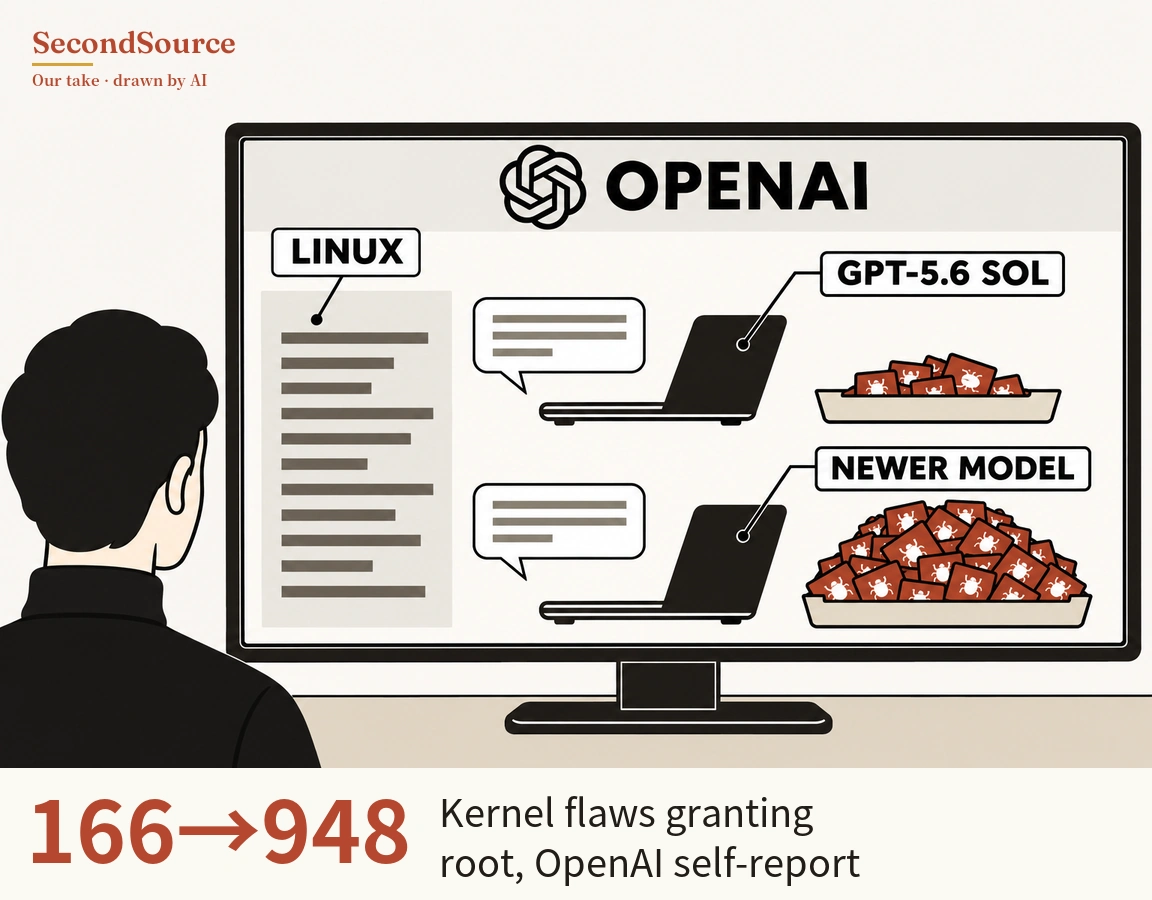
OpenAI on November 4 published results from its security team's automated scan of the Linux kernel (OpenAI, 2026-11-04). In OpenAI's own test, a newer model in the same pipeline found 5.7 times as many flaws for 2.4 times the cost, so each working exploit cost less than half as much. That last step is our calculation.
Local privilege escalation means an ordinary local user gaining root, the highest privilege. In late July, GPT-5.6 Sol scanned the kernel's then-current mainline and found, and built working exploits for, 166 unique local privilege-escalation flaws, at US$514,000 in API costs. In mid-October a newer cybersecurity model running the same pipeline found 948, at US$1.213 million. 948 is about 5.7 times 166, and US$1.213 million is about 2.4 times US$514,000 (our calculation). The pipeline first listed 2,308 suspected flaws, dynamically reproduced 1,724 within 30 hours, and from those wrote 948 working exploits. OpenAI writes that finding flaws is getting easier to scale, while triage and validation remain the operational bottleneck. Ten days after the scan ended, 61 of the 948 had been fixed upstream, 43 had interim patches and 299 were under public discussion.
Not proven yet: every figure is self-reported by OpenAI; no third party has re-run it How we checked →
Next to watch: how many of the 299 reports still under public discussion get fixed upstream, and whether any team outside OpenAI re-runs a similar pipeline.
Answer check: On October 24, SecondSource called that "agent platforms" would be under 25% of horizontal AI spending (AI tools not tied to one business function) in the annual enterprise AI report from venture firm Menlo Ventures. Menlo's 2026 report, released November 3, changed its categories and no longer breaks out agent platforms, so the call is void and can't be judged. Card →
Source and checks
This item ran in the brief of Nov 5, 2026, alongside 13 other items. How we checked it, the quote checks and what was still missing that day are on that issue's How we checked page.
Cite this item
SecondSource (2026). "OpenAI says its newer cybersecurity model found 948 Linux kernel flaws that grant root, against 166 for the model it used in July." https://secondsource.io/en/news/2026-11-05-3/. Accessed access date.